An authenticated user with access to the admin console can execute arbitrary operating system commands.
./recon.sh --target self
Gabriel Hinostroza
Penetration Tester · Web, API, Android, Active Directory
Penetration tester focused on web applications, APIs, Android and Active Directory infrastructure. I report what I find through coordinated disclosure, and publish the analysis once the fix is out.
CRITICAL CVE
CVE-2026-2586
9.1
Eclipse GlassFish · Authenticated RCE · Published
04
CVEs filed
9.1
top CVSS
11
write-ups
What I work on and how I disclose it.
I work on web applications, APIs, Android and Active Directory infrastructure. Most of what I find comes from reading code and protocols carefully rather than from running scanners.
Everything I report goes through coordinated disclosure, and I publish the write-up once the fix is out — the finding is only half the work.
Coordinated disclosure. Click through for the full analysis.
The File Manager does not verify that the session identifier belongs to the authenticated user, which chains into remote code execution.
The File Manager's path parameter accepts command substitution syntax.
The database export exposes any user's password reset codes, allowing the takeover of other accounts.
Built while testing, because I needed them.
Introspector
PythonOut-of-band operations framework. HTTP and DNS callbacks with correlation tokens that tell you which injection point fired, DNS exfiltration decoding, payload hosting and byte-exact responses for what a real HTTP server refuses to send.
GlassFish Research
CVE-2026-2586The research behind the authenticated RCE in Eclipse GlassFish: how the admin console reaches command execution.
Termix Research
CVE-2026-45746 · 45750Two findings in Termix — broken access control and command injection — chained into remote code execution.
Original research and Hack The Box machines, start to finish.
Original research, not a lab.
Tabby
HTBTomcat manager to host compromise.
Blackfield
HTBActive Directory, start to finish.
Offensive security, web and mobile.
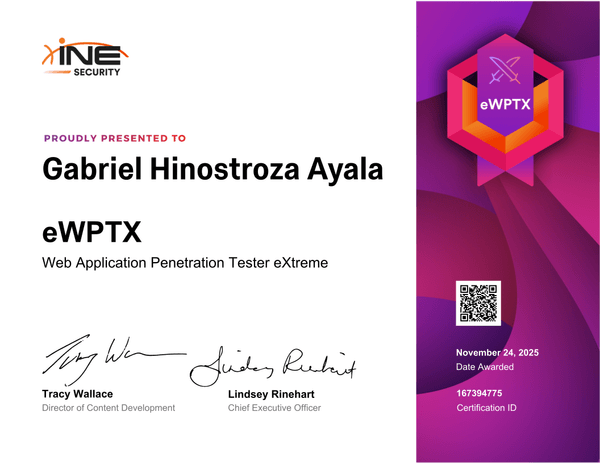
eWPTXv3
INEWeb Application Penetration Tester eXtreme.
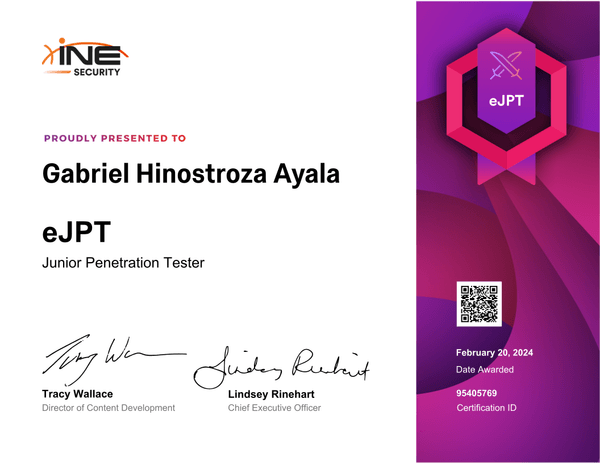
eJPTv2
INEJunior Penetration Tester.
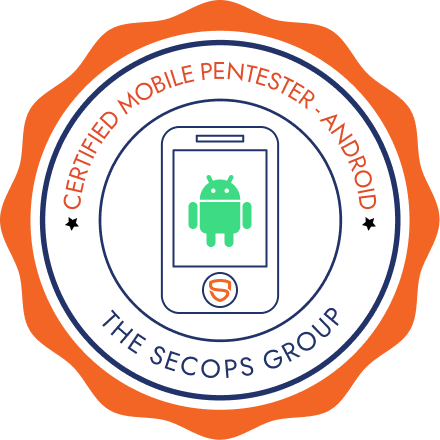
CMPen-Android
SecOps GroupCertified Mobile Pentester – Android.
06
Get in touch
Decode the key.
Base64 · Decode the payload and use the result as the email subject.
-----BEGIN OPENSSH PRIVATE KEY-----
b3BlbnNzaC1rZXktdjEAAAAABG5vbmUAAAAEbm9uZQAAAAAAAAAB
AAAAMwAAAAtzc2gtZWQyNTUxOQAAACBHYWJyaWVsSEExMmNoYWxs
ZW5nZS1lbnVtZXJhdGlvbi1iYXNlNjQAAAAEc2VjcmV0AAAA
Y2hhbGxlbmdlOiBlbnVtZXJhdGlvbg==
AAAAC3NzaC1lZDI1NTE5AAAAIEdINFMtcmVzZWFyY2gtb25seQ==
-----END OPENSSH PRIVATE KEY-----